Finance & Fintech
Regulated speed.
Startup velocity.
Ship PCI-adjacent, audited workloads without a months-long infrastructure project.
Your data stays in your cloud — Bunnyshell never touches it.
We'll answer your security questionnaire
 Helm
 Docker
 Terraform
 K8s
 EKS
 AKS
 GKE
 SOC 2
 ISO 27001
 ISO 9001
Trusted by over 30,000 engineers from
“Manual tests on Argo CD PRs now take me seconds. When you review dozens of PRs a day, that's a game-changer.”

“Automatically created a Bunnyshell environment based on PRs, speeding up the entire task implementation process.”
“The automation and scalability that Bunnyshell provides complements the DigitalOcean platform, empowering developers to build amazing products.”
$ cat how-it-works.md
How Bunnyshell works
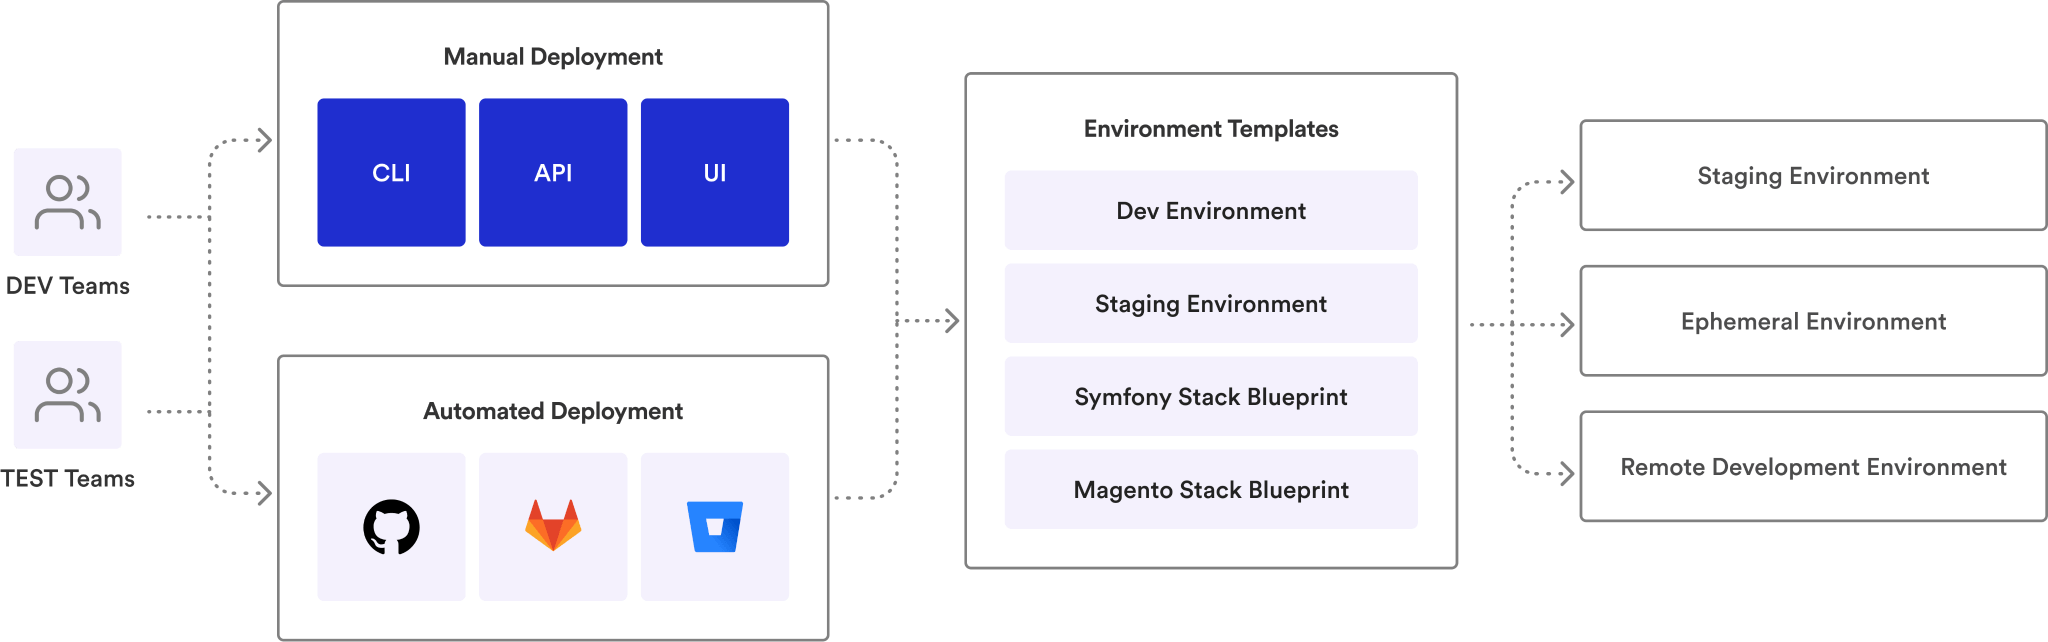
Connect your repo
Link your GitHub, GitLab, or Bitbucket repository. Define your environment using Docker Compose, Helm, or Terraform — tools your platform team already runs.
 GitHub
 GitLab
 Bitbucket
 Docker
 Helm
 K8s
Open a pull request
Bunnyshell auto-provisions an isolated, full-stack environment for every PR — same compliance posture as production, in your own cloud account.
Merge and move on
Tests pass, code is reviewed, PR merges. The environment auto-destroys — logged, auditable, no manual cleanup.
Built for regulated data.
Compliant by default.
Bunnyshell meets the security and compliance bar your finance or fintech engineering team needs. Customer data, source code, and databases never leave your own cloud account — we orchestrate, you own everything.
BYOC Architecture
Bring Your Own Cloud. Bunnyshell never stores your source code, cardholder data, or transaction records. Everything runs inside your own Kubernetes cluster.
Namespace Isolation
Every environment runs in a dedicated Kubernetes namespace — no shared tenancy between teams, products, or legal entities.
Secrets Encryption
All environment variables, API keys, and database credentials are encrypted at rest and in transit. No hard-coded secrets, ever.
IP Whitelisting
Restrict preview environment access to approved IP ranges — keep test environments with real-shaped financial data off the open internet.
Full Audit Logging
Every deploy, sleep, and teardown is logged — who did what, when, and where. Exportable for SOC 2 and internal audit evidence.
SSO Integration
SAML and OIDC support for your identity provider. Your existing access policies extend to Bunnyshell automatically.
Approval Workflows, Not Tribal Knowledge
Production and audit-relevant environments can require explicit sign-off before a deploy proceeds — with the requester, approver, and linked change ticket all captured automatically. When an auditor asks "who approved this," the answer is a record, not a memory.
- ✓Environment locks — lock production and audit-scoped environments against accidental or unreviewed changes
- ✓Approval workflows — require platform team or compliance sign-off before a deploy proceeds
- ✓Rollback on failure — automatic rollback to the last healthy deployment if health checks fail post-deploy
- ✓Change audit trail — every change logged with who, what, when, and the approval chain — exportable for evidence
Drift Is How "It Passed Staging" Becomes an Incident
A config that quietly diverges between staging and production is how compliant code ships into a non-compliant environment. Bunnyshell flags the divergence the moment it happens, with a line-by-line diff — not a postmortem six months later.
- ✓Auto-detection — notified the moment an environment drifts from its approved template
- ✓Built-in diff editor — review exactly what changed — line by line, component by component
- ✓One-click sync — pull template updates into your environment or formally acknowledge the divergence
- ✓Version tracking — see which template version each environment is running against — audit-ready
Also Built In
What else your team stops maintaining.
DORA Metrics, No Extra Tooling
Cycle Time and Deployment Frequency, per repository, built in — a real number for the board, not an anecdote.
Cost Governance
Auto-sleep, auto-destroy, and per-environment cost tracking via Kubecost, so compliance testing spend stays predictable.
High Availability in Production
Horizontal autoscaling, multi-region deployment, and automated failover for the environments customers actually use.
Case Studies
Trusted by Financial Services
Teams Like Yours.
Trusted by engineering teams
shipping fast
“Manual tests on Argo CD PRs now take me seconds. When you review dozens of PRs a day, that's a game-changer.”
“Automatically created BunnyShell environment based on PRs, speeding up the entire task implementation process.”
“The automation and scalability that Bunnyshell provides complements the DigitalOcean platform, empowering developers to build amazing products.”
“Websites don't die anymore, sales keep growing sustained by state-of-the-art tech scalability. Customers send thank you cards.”
“From a release once in 2-4 weeks to multiple times per week, and nobody's stressed about it.”
“I can count on an integrated platform for managing our infrastructure — capabilities we don't have in-house, at a fraction of the cost.”
“I can do with Bunnyshell and a DevOps person what my clients are doing with 4 DevOps people.”
“Developers want convenience. They expect someone to translate their Docker Compose to the cloud. They're not going to rush to learn Kubernetes.”
“Bunnyshell was the only tool that handled our Helm + EKS setup without asking us to change everything.”
“60+ microservices. Bunnyshell deploys them in parallel and lets us control which ones come first.”
Book a Demo. Talk to our team about your compliance requirements.
Get a walkthrough tailored to your stack, your regulatory obligations, and your existing CI/CD. No generic pitch.
Frequently asked
questions
Can’t find what you’re looking for? Talk to our team
No. Bunnyshell uses a BYOC (Bring Your Own Cloud) model. Your source code, databases, and transaction data stay in your cloud account and container registry at all times. Bunnyshell orchestrates deployments via a lightweight agent — we never store or access your data.