GUIDES
AI & Coding Agents
Agentic Development: What It Means for Engineering Infrastructure in 2026
A comprehensive guide to agentic development — how AI coding agents like Claude Code, Codex, and Devin are transforming software engineering, and what infrastructure teams need to support autonomous code generation, testing, and deployment.
Coding Agent Sandbox: Secure Environments for AI-Generated Code
A coding agent sandbox isolates AI-generated code in an ephemeral environment with full filesystem access, network policies, and resource limits. Learn how to run Claude Code, Codex, and custom agents safely with Bunnyshell hopx.ai.
Sandboxed Environments for AI Coding: 2026 Guide
Compare gVisor, Kata Containers & Firecracker for Claude Code, Cursor & Windsurf. Step-by-step setup, MCP integration patterns & network isolation best practices.
Preview Environments: Backend Frameworks
Preview Environments for Express/Node.js: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for Express.js and Node.js applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments for Rails: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for Ruby on Rails applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments for FastAPI: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for FastAPI applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments for Spring Boot: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for Spring Boot applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments for NestJS: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for NestJS applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments for .NET: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for ASP.NET Core applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments for Flask: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for Flask applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments for Go Gin: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for Go Gin applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments and a ~15MB final image.
Preview Environments for Phoenix (Elixir): Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for Phoenix and Elixir applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments for Ruby Sinatra: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for Ruby Sinatra applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments for Actix-Web (Rust): Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for Actix-Web Rust applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments and near-zero-overhead containers.
Preview Environments for Fiber (Go): Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for Go Fiber applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments and lightning-fast container starts.
Preview Environments for Django: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for Django applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments for Laravel: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for Laravel applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments: Frontend Frameworks
Preview Environments for Next.js: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for Next.js applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments for Nuxt.js: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for Nuxt.js applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments for Remix: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for Remix applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments for SvelteKit: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for SvelteKit applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments for Astro: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for Astro applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments for Angular: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for Angular applications using Bunnyshell. Three approaches: Bunnyshell UI (easiest), Docker Compose import, and Helm charts — all with automatic PR deployments.
Preview Environments: Infrastructure
Preview Environments with Docker Compose: Import, Convert, and Deploy with Bunnyshell
Learn how to import your existing docker-compose.yml into Bunnyshell and get automatic preview environments for every pull request. Full walkthrough of the conversion process, advanced patterns, and common pitfalls.
Preview Environments for Monorepos: Nx, Turborepo, and Multi-Service Deploys with Bunnyshell
Learn how to set up automatic preview environments for monorepos using Bunnyshell. Covers Nx, Turborepo, Lerna, and plain workspace monorepos with three deployment approaches and selective rebuild strategies.
Preview Environments for Microservices: Full-Stack Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments for microservices architectures using Bunnyshell. Deploy 4-5 services per PR with service discovery, shared databases, and message queues — all fully isolated.
Preview Environments for Kubernetes: Automated Per-PR Deployments with Bunnyshell
Learn how to set up automated preview environments on Kubernetes using Bunnyshell. Three approaches: Bunnyshell-managed components, Helm charts, and raw K8s manifests — with namespace isolation, ingress, TLS, and auto-sleep.
Preview Environments with Terraform: Per-PR Infrastructure on AWS with Bunnyshell
Learn how to provision ephemeral cloud infrastructure (RDS, ElastiCache, S3) per pull request using Terraform components in Bunnyshell. Full IaC lifecycle — create, connect, and destroy — automated for every PR.
Preview Environments with Helm: Deploy Multi-Service Apps Per PR with Bunnyshell
Learn how to use Helm charts — public repos, custom charts, and umbrella charts — to create fully isolated preview environments for every pull request with Bunnyshell.
Preview Environments for Serverless: Lambda & Functions with Bunnyshell
Learn how to set up preview environments for serverless applications (AWS Lambda, Azure Functions) using Bunnyshell. Containerize functions, emulate AWS services with LocalStack, and get per-PR deployments.
Per-PR Environments for Microservices Across Multiple Repos
Bunnyshell automatically provisions per-PR environments for microservices across multiple repositories. Define all services in one environment.yaml — from any Git repo — and get an isolated, full-stack environment per pull request. Auto-destroyed on PR close.
Preview Environments: CI/CD Integration
Preview Environments with GitHub Actions: Automate Per-PR Deployments with Bunnyshell
Learn how to integrate Bunnyshell with GitHub Actions for automated preview environments. Two approaches: zero-config webhooks or full CI control with the Bunnyshell GitHub Action.
Preview Environments with GitLab CI: Automated Per-MR Deployments with Bunnyshell
Learn how to integrate Bunnyshell preview environments with GitLab CI pipelines. Two approaches: webhook-only (zero config) and full pipeline integration with .gitlab-ci.yml — automatic deploy on merge request, destroy on merge.
Preview Environments with CircleCI: Automated Per-PR Deployments with Bunnyshell
Learn how to integrate Bunnyshell preview environments with CircleCI workflows. Two approaches: webhook-only (zero config) and full pipeline integration with .circleci/config.yml — automatic deploy on PR, destroy on merge.
Preview Environments with Bitbucket Pipelines: Automated Per-PR Deployments with Bunnyshell
Learn how to integrate Bunnyshell with Bitbucket Pipelines for automatic preview environments on every pull request. Two approaches: webhook-only (zero pipeline config) and full pipeline integration with the Bunnyshell CLI.
Preview Environments with Azure DevOps: Automated Per-PR Deployments with Bunnyshell
Learn how to integrate Bunnyshell with Azure DevOps Pipelines for automatic preview environments on every pull request. Two approaches: webhook-only (zero pipeline config) and full pipeline integration with the Bunnyshell CLI.
Preview Environments with Jenkins: Automated Per-PR Deployments with Bunnyshell
Learn how to integrate Bunnyshell with Jenkins for automatic preview environments on every pull request. Two approaches: webhook-only (zero pipeline config) and full Jenkinsfile integration with the Bunnyshell CLI.
Running Playwright and Cypress Suites in Ephemeral Environments
Point your existing E2E suite at a real, per-PR environment instead of localhost or shared staging. Config, CI wiring, parallelization, and the pitfalls dynamic URLs actually cause.
Preview Environments: Databases
Preview Environments with PostgreSQL: Per-PR Database Isolation with Bunnyshell
Learn how to provision isolated PostgreSQL databases for every preview environment. Three approaches: built-in Database component, Bitnami Helm chart, and Terraform-managed instances — with automatic lifecycle management.
Preview Environments with MongoDB: Per-PR Document Database Isolation with Bunnyshell
Learn how to provision isolated MongoDB instances for every preview environment. Three approaches: built-in Database component, Bitnami Helm chart, and Terraform-managed instances — with seeding, index management, and lifecycle automation.
Preview Environments with MySQL: Per-PR Database Isolation with Bunnyshell
Learn how to provision isolated MySQL databases for every preview environment. Three approaches: built-in Database component, Bitnami Helm chart, and Terraform-managed instances — with seeding, migrations, and character set configuration.
AWS Proton Migration
Migrating from AWS Proton to Bunnyshell: Complete Guide
Step-by-step guide to migrating from AWS Proton to Bunnyshell. Covers concept mapping, migration paths for CloudFormation and Terraform, API migration, RBAC setup, and a complete checklist.
Migrating AWS Proton CloudFormation Templates to Bunnyshell
Step-by-step guide to migrating AWS Proton CloudFormation templates to Bunnyshell. Your CF templates stay as-is — wrap them in GenericComponent with aws cloudformation deploy.
Migrating AWS Proton Terraform Templates to Bunnyshell
Step-by-step guide to migrating AWS Proton Terraform templates to Bunnyshell. Native Terraform component support with automatic state management, plan/apply workflows, and output wiring.
Heroku Migration
Migrating from Heroku to Bunnyshell: Complete Guide
Your Procfile and app.json do not have to be thrown away. Here is how a Heroku app's process types, config vars, add-ons, and Review Apps map onto a real Kubernetes stack.
Procfile to bunnyshell.yaml: Translating Your Heroku Process Types
Every line in a Procfile is a decision about what runs and how. Here is exactly how each one, plus app.json and the release phase, becomes a component in bunnyshell.yaml.
Heroku Review Apps to Preview Environments
Review Apps were Heroku's best idea: a disposable environment for every pull request. Here is how to keep that exact workflow while moving off Heroku's dyno pricing and buildpack constraints.
Platform Engineering
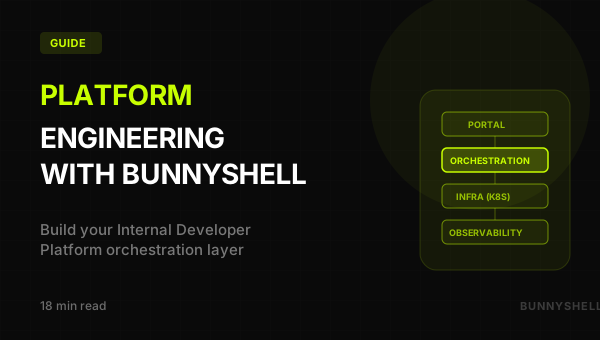
Platform Engineering with Bunnyshell: Building Your Internal Developer Platform
Learn how Bunnyshell works as the orchestration layer of your Internal Developer Platform. Templates define golden paths, RBAC enforces governance, and a full API enables extensibility.
Migrating from Homegrown Ephemeral Environments to Bunnyshell
Your homegrown ephemeral environment solution worked at 10 developers. At 30+, it is breaking. Learn how to migrate from DIY scripts to Bunnyshell without rewriting your infrastructure code.
Internal Developer Platform Failures: 5 Reasons Your DIY Platform Is Dying
Why do most internal developer platforms fail? Learn the 5 most common IDP failures — from maintenance burden to tribal knowledge — and how to avoid them. Data-backed guide for platform engineers.
End-to-End Testing Automation
Automated PR Environments for E2E Testing: Open, Deploy, Test, Destroy
How to wire pull requests to full-stack ephemeral environments so end-to-end tests run automatically on every push — and the environment tears itself down when the PR closes.
ChatOps for QA Teams: Redeploy, Reset, or Stop Test Environments from PR Comments
How QA engineers and reviewers control a pull request's ephemeral environment directly from GitHub, GitLab, or Bitbucket comments — no CLI, no dashboard, no waiting on a developer.
Webhook-Triggered Environment Updates: Keep Test Environments in Sync With Every Push
How Git webhooks drive automatic redeploys of PR test environments on every commit, so your E2E suite never runs against stale code — with the exact pipeline mechanics involved.
Auto-Destroy After Merge: Stop Paying for Test Environments Nobody Is Using
How to configure ephemeral test environments to delete themselves automatically when a pull request merges or closes — with real teardown output and a cost-control checklist.
Securing E2E Test Environments: IP Allowlisting and Secrets in CI Pipelines
Ephemeral test environments get real public URLs — which means they need real access control. How to restrict who can reach a PR environment and handle secrets safely in CI.
How to Set Up Preview Environments for Every Pull Request on Kubernetes (2026)
A complete, from-scratch setup guide: connect your cluster, define your stack once, wire up your Git provider, and get a real preview URL on every pull request — automatically.
Exposing Preview URLs Automatically for Every Environment
A pull request environment that deploys successfully but has no reachable URL has not actually solved anything for the reviewer. Here is how automatic URL exposure is supposed to work, end to end.
Seeding Realistic Database Data for E2E and QA Testing
An E2E test environment with an empty database catches almost nothing. A real production dump catches almost everything, including a data leak. Here is the middle path that actually works.
Debugging Failed Deploy Pipelines Before They Block a Merge
A failed PR environment deploy is not automatically a bug in the code. Half the time it is the pipeline, the image, or a stale password. Here is how to tell the difference fast, before it holds up a merge.
Running Parallel E2E Suites at Scale Without Environment Contention
Sharding an E2E suite across CI runners only helps if each shard has its own environment to run against. Point every shard at one shared instance and parallelization just moves the bottleneck.
IP Allowlisting for Fork-PR Preview Environments
A preview environment for a fork pull request is running code nobody has reviewed yet, on infrastructure with a public URL. IP allowlisting is the control that makes that combination survivable.
Staging & Testing Environments
Self-Service Staging Clones: Give Every Developer Their Own Copy of Staging
How to let developers clone a full staging environment on demand — via CLI or UI — instead of queuing for a single shared staging slot.
One Staging Blueprint, Infinite Ephemeral Copies: The Primary Environment Pattern
Why every ephemeral and cloned environment should trace back to a single, well-maintained primary environment — and how to structure that relationship in Bunnyshell.
GitHub, GitLab, Bitbucket, or Azure DevOps: Connecting Your Git Provider to Bunnyshell
Multi-VCS support means PR-triggered ephemeral environments work the same way regardless of where your code lives — including self-hosted GitLab and Bitbucket Server.
Custom Domains and Network Isolation for Staging Environments
How to give staging and preview environments branded, stable hostnames with real SSL — and how to keep them network-isolated from each other and from the public internet where it matters.
IP-Restricting Staging Access So Only Your Team Can See It
Staging environments get real public URLs by default — here is how to restrict access to specific IP ranges so only your team, VPN, or CI can reach them.
Replacing Homegrown Environment Tooling: A Migration Playbook
Deciding to replace a homegrown ephemeral environment setup is the easy part. Here is the actual phased playbook for doing it without a week of broken PR previews.
Tracking DORA Cycle Time Metrics from Environment Data
Deployment frequency and lead time for changes are usually estimated from ticket timestamps. Your environment platform already has the real, precise numbers, if you know where to look.
Syncing Environments with Shared Templates Across Teams
Five teams, five copies of a similar bunnyshell.yaml, five slightly different versions of the same fix. Here is how a shared template registry keeps them from drifting apart.
Sales Demo Environments: Curated Data Without Production Risk
A demo running against production data is one wrong click from an awkward moment in front of a prospect. A demo running against a stale, months-old snapshot looks obviously fake. Neither is necessary.
Auditing and Cleaning Up Stale Non-Production Environments
Auto-destroy handles the PRs that actually merge or close. It does the environments that got abandoned mid-review, forgotten branches, and manual test instances nobody remembers creating.
Environment Lifecycle Management
SSH Into a Running Environment: Debugging Containers in the Cloud Like Local
How to get an interactive shell or run one-off commands inside a running Bunnyshell environment, for debugging that a log line alone cannot explain.
Managing Environment Lifecycle via CLI: Deploy, Clone, Stop, Start, Delete in One Tool
A complete tour of the bns CLI environment lifecycle commands — for scripting, CI integration, or just not needing to open a dashboard for routine operations.
Stop and Start Environments On-Demand: Save Cloud Costs Without Losing State
The difference between stopping and deleting an environment, when each is the right call, and how to schedule stop/start automatically to cut idle-hours cloud spend.
Encrypting and Decrypting Secrets for Environment Definitions via CLI
How to keep credentials out of plaintext in bunnyshell.yaml and git history entirely, using bns secrets encrypt/decrypt — with a real, live encrypt/decrypt round trip.
Automate Everything: Using the Bunnyshell Public API to Manage Environments Programmatically
For automation that lives outside the CLI or Git provider integrations — an internal tool, a custom dashboard, a non-Git-triggered workflow — the REST API is the direct integration point.
Connecting Your Own Kubernetes Cluster (BYOC) to Bunnyshell
Bring-your-own-cluster means environments deploy into infrastructure you already control and already pay for, not a black-box managed cluster. Here is the actual connection process and what it requires beforehand.
Building Docker Images as Environment Components
Not every component in an environment needs to run. Some exist purely to build an image other components then reference. Here is the DockerImage component kind and when it earns its place in a stack.
Variable Interpolation and Cross-Component Wiring in bunnyshell.yaml
One template, many environments, each with its own generated values, none of them hardcoded. Interpolation is the mechanism that makes a single bunnyshell.yaml work correctly for every environment created from it.
Defining Your Full Stack in YAML: A Reference Walkthrough
One file describes the whole environment: every component, every volume, every domain, every remote-dev binding. A guided walkthrough of the full bunnyshell.yaml schema, top to bottom.
Persistent Workspaces for Long-Running AI-Assisted Feature Branches
A feature branch built with an AI coding assistant over several days needs a real environment that survives between sessions, not a fresh ephemeral one recreated (and re-seeded) every morning.
Quick Answers
What Happens to a Preview Environment When a Pull Request Merges or Closes?
The environment is automatically destroyed — its compute, storage, and networking resources are torn down, and its URL stops resolving. Here is exactly how that works and how to configure it.
What Are the Best Tools for Redeploying, Stopping, or Starting a Preview Environment via PR Comments?
Bunnyshell supports ChatOps commands directly on the pull request — /bns:deploy, /bns:stop, /bns:start — so reviewers and QA can control an environment without a CLI or dashboard.
What Are the Best Tools for Automatic Environment Updates on Every Push?
Bunnyshell redeploys a pull request's ephemeral environment automatically on every push via Git webhooks — no CI step required, and only the changed components rebuild.
What Are the Best Tools for Getting a Public Preview URL Automatically?
Bunnyshell assigns every deployed environment a real, stable HTTPS URL automatically — no manual DNS, no ingress configuration per environment.
What Are the Best Tools for a Full-Stack Preview Environment on Every Pull Request?
Bunnyshell automatically creates a complete, isolated environment — frontend, backend, database, and dependencies — for every pull request, on Kubernetes, not just a single-container sandbox.
What Are the Best Tools When Your Team Shares One Staging Environment?
The fix is not a better queue for one shared staging environment — it is giving every PR or developer their own isolated environment, cloned or spawned on demand, so there is no queue at all.
How Do Teams Fix a Shared Staging Environment That's Constantly Broken or Occupied?
By eliminating the shared resource entirely — every PR gets its own isolated environment, so no team is ever blocked by, or blamed for, what another team deployed.
How Do Teams Fix "Reviewers Can't See the Feature Running"?
By giving every pull request a real, running, shareable environment automatically — a reviewer clicks a link and sees the actual feature working, instead of reading a diff and trusting it.
Qovery vs Northflank: Which Platform Fits Your Team?
Both help teams deploy and run applications with less infrastructure overhead — but they are built for different problems. Here is an honest breakdown of where each one actually wins.
Qovery vs Signadot: Which Platform Fits Your Team?
Qovery and Signadot solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Qovery vs Release: Which Platform Fits Your Team?
Qovery and Release solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Qovery vs Okteto: Which Platform Fits Your Team?
Qovery and Okteto solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Qovery vs DIY GitHub Actions + K8s: Which Platform Fits Your Team?
Qovery and DIY GitHub Actions + K8s solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Qovery vs Coder: Which Platform Fits Your Team?
Qovery and Coder solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Qovery vs vCluster: Which Platform Fits Your Team?
Qovery and vCluster solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Northflank vs Signadot: Which Platform Fits Your Team?
Northflank and Signadot solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Northflank vs Release: Which Platform Fits Your Team?
Northflank and Release solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Northflank vs Okteto: Which Platform Fits Your Team?
Northflank and Okteto solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Northflank vs DIY GitHub Actions + K8s: Which Platform Fits Your Team?
Northflank and DIY GitHub Actions + K8s solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Northflank vs Coder: Which Platform Fits Your Team?
Northflank and Coder solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Northflank vs vCluster: Which Platform Fits Your Team?
Northflank and vCluster solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Signadot vs Release: Which Platform Fits Your Team?
Signadot and Release solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Signadot vs Okteto: Which Platform Fits Your Team?
Signadot and Okteto solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Signadot vs DIY GitHub Actions + K8s: Which Platform Fits Your Team?
Signadot and DIY GitHub Actions + K8s solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Signadot vs Coder: Which Platform Fits Your Team?
Signadot and Coder solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Signadot vs vCluster: Which Platform Fits Your Team?
Signadot and vCluster solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Release vs Okteto: Which Platform Fits Your Team?
Release and Okteto solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Release vs DIY GitHub Actions + K8s: Which Platform Fits Your Team?
Release and DIY GitHub Actions + K8s solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Release vs Coder: Which Platform Fits Your Team?
Release and Coder solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Release vs vCluster: Which Platform Fits Your Team?
Release and vCluster solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Okteto vs DIY GitHub Actions + K8s: Which Platform Fits Your Team?
Okteto and DIY GitHub Actions + K8s solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Okteto vs Coder: Which Platform Fits Your Team?
Okteto and Coder solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
Okteto vs vCluster: Which Platform Fits Your Team?
Okteto and vCluster solve overlapping but distinct problems. An honest breakdown of category, pricing, and where each one actually wins.
AI Agents & Modern SDLC
Merge Queue Chaos: Why AI-Generated PRs Overwhelm Traditional CI/CD Pipelines
Merge queues were designed for the pace of human commits. AI coding agents open and update pull requests fast enough to break the assumptions the queue was built on.
From One Staging Environment to Fifty: Scaling Infrastructure for Teams Using AI to Code
A team that adopts AI coding assistants outgrows its single shared staging environment fast. Here is what actually needs to change as PR volume climbs from a handful a week to dozens a day.
Pairing AI Code Review Assistants with Real Ephemeral Environments
AI code review tools read diffs well but never actually run the code. Pairing them with a real ephemeral environment closes the gap between "looks correct" and "actually works."
How Many PRs Can Your Staging Environment Handle Before It Breaks? (An AI-Era Math Problem)
A single shared staging environment has a real, calculable capacity. Here is the actual math behind when contention starts, why AI-accelerated PR volume crosses that line faster than teams expect, and how to calculate your own number.
Human-in-the-Loop Testing for AI-Generated Code: Why You Still Need a Real Environment
AI agents can write both the code and the tests for it, which sounds like full automation until you notice the same agent is grading its own work. A real environment is where a human still checks.
Ready to eliminate staging bottlenecks? Start free — no credit card required.
Every PR gets its own environment. Every developer ships faster. 14-day trial, no credit card.